Blog
Insights and articles from cybersecurity experts
The leader in cyber security in Thailand with innovative platforms and world-class team of experts
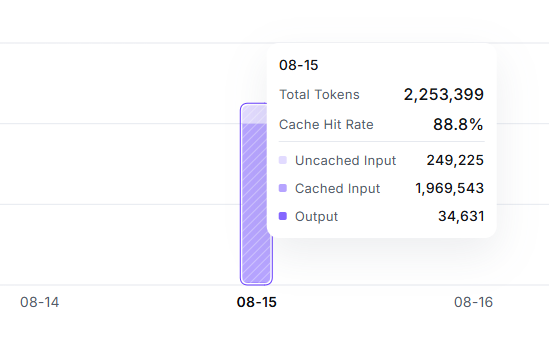
The setup The brief I gave it was one sentence: pentest this internal web app, blackbox, dev environment, I’m already...
Even well-trained employees make mistakes. They may save passwords in Notepad, use unsafe Wi-Fi, click phishing links, or download free...

Inside the Damage Businesses May Never Fully Recover From When company data appears on the Dark Web, many people think...

Thai Organizations Still Test on a Schedule While Attackers Hunt Every Second What Is Continuous Threat Exposure Management, and Why...

Has Your Organization Closed Last Month’s Microsoft Vulnerabilities? Tomorrow is Microsoft Patch Tuesday for July 2026. For many...

It Is an Investment in Trust, Revenue, and Business Growth. Your website may load perfectly. Your app may work smoothly...
The setup The brief I gave it was one sentence: pentest this internal web app, blackbox, dev environment, I’m already...
Even well-trained employees make mistakes. They may save passwords in Notepad, use unsafe Wi-Fi, click phishing links, or download free...
Inside the Damage Businesses May Never Fully Recover From When company data appears on the Dark Web, many people think...
Thai Organizations Still Test on a Schedule While Attackers Hunt Every Second What Is Continuous Threat Exposure Management, and Why...
Has Your Organization Closed Last Month’s Microsoft Vulnerabilities? Tomorrow is Microsoft Patch Tuesday for July 2026. For many...
It Is an Investment in Trust, Revenue, and Business Growth. Your website may load perfectly. Your app may work smoothly...

What Should an Organisation Do After a Ransomware Attack? The First 24 Hours When ransomware hits, the problem is not...

Start Using the Internet Safely and Feel Confident Every Time You Connect How important is safe internet use? The online...

Robust cybersecurity can be brought down by just a single person. Cybersecurity awareness is far more critical than often realized...

A Cyber Threat Every Organisation Must Prepare For Ransomware is a type of malware that encrypts an organisation’s files or...

What Digital Asset Businesses Need to Know A smart contract is not just code. It can define rights, transfers, access...

PDPA Section 37 and Cybersecurity What Technical Measures Should Organisations Have? PDPA is not only about privacy documents. It also...

A good pentest should not stop at a PDF report. It should show what can actually be exploited, what matters...

Finding vulnerabilities is only the first step. The real value comes from fixing the right risks faster. Many organisations receive...
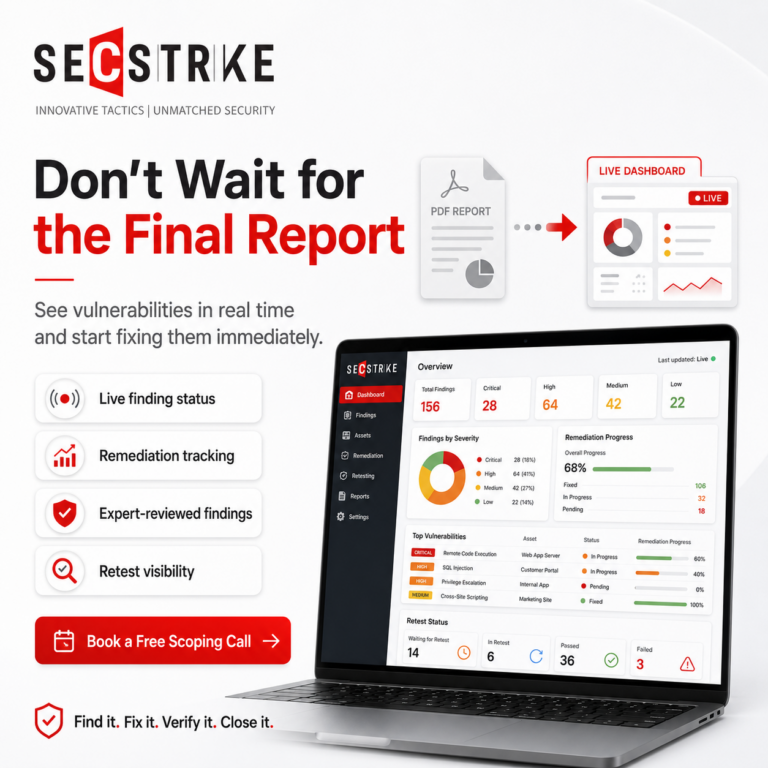
Why wait for the final report when your IT team can see vulnerabilities in real time and start fixing them...
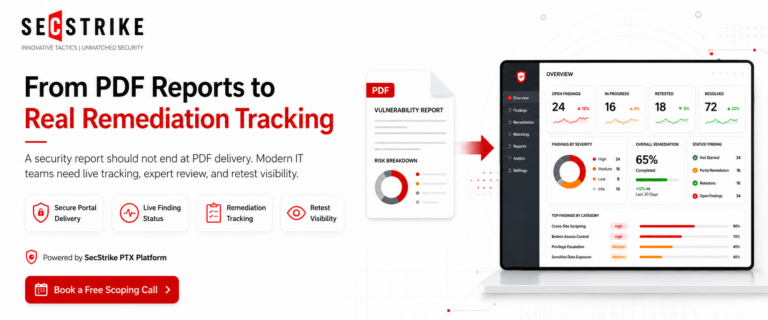
A security report should not end at “PDF delivered.” It should help your team track, fix, retest, and close real...
Cyber Attack Analysis: How Hackers Penetrate Systems — and Where to Defend First Introduction: Most Attacks Start With a Door...
Introduction: APIs Are Now One of Your Biggest Business Attack Surfaces APIs sit behind almost every digital experience your business...
Your web application may look completely normal. Customers can log in.APIs are working.The dashboard loads.Nothing is crashing. But here is...
The OWASP Top 10 Is a Good Place to Start Finding the Answer If your business runs a web application...

Your system passed last year’s pentest. But is it still secure today? That is the question more IT leaders should...

A Pentest Audit, or penetration test, is not simply about “trying to hack” your organization’s systems. It is a controlled...

What Is the Difference Between Pentest and VA Scan? Confused between Pentest and VA Scan? This guide explains the difference...

What Is Penetration Testing (Pentest)? Why Thai Organisations Need It and How to Get Started A professional English translation of...

ในโลกที่ภัยคุกคามไซเบอร์ซับซ้อนขึ้นทุกวัน การตัดสินใจเลือกบริษัททำ Vulnerability Assessment (VA) หรือ Penetration Testing (Pentest) สำหรับ...

OVERVIEW Cisco has disclosed a critical authentication bypass vulnerability in Cisco Catalyst SD-WAN Controller (formerly vSmart) and Cisco...

Tillywork versions v0.1.3 and below are affected by a critical SQL Injection vulnerability. This flaw is specifically located within the...

In an era of rapidly evolving cyber threats, traditional security testing is no longer enough. Pentest as a Service (PtaaS) is emerging as...